Insights Posture & Benchmark
Your posture score from 0 to 100, reassessed every 6 hours and compared with NIST CSF, CIS Controls, OWASP and MITRE ATT&CK.
Reassessed every 6 hours
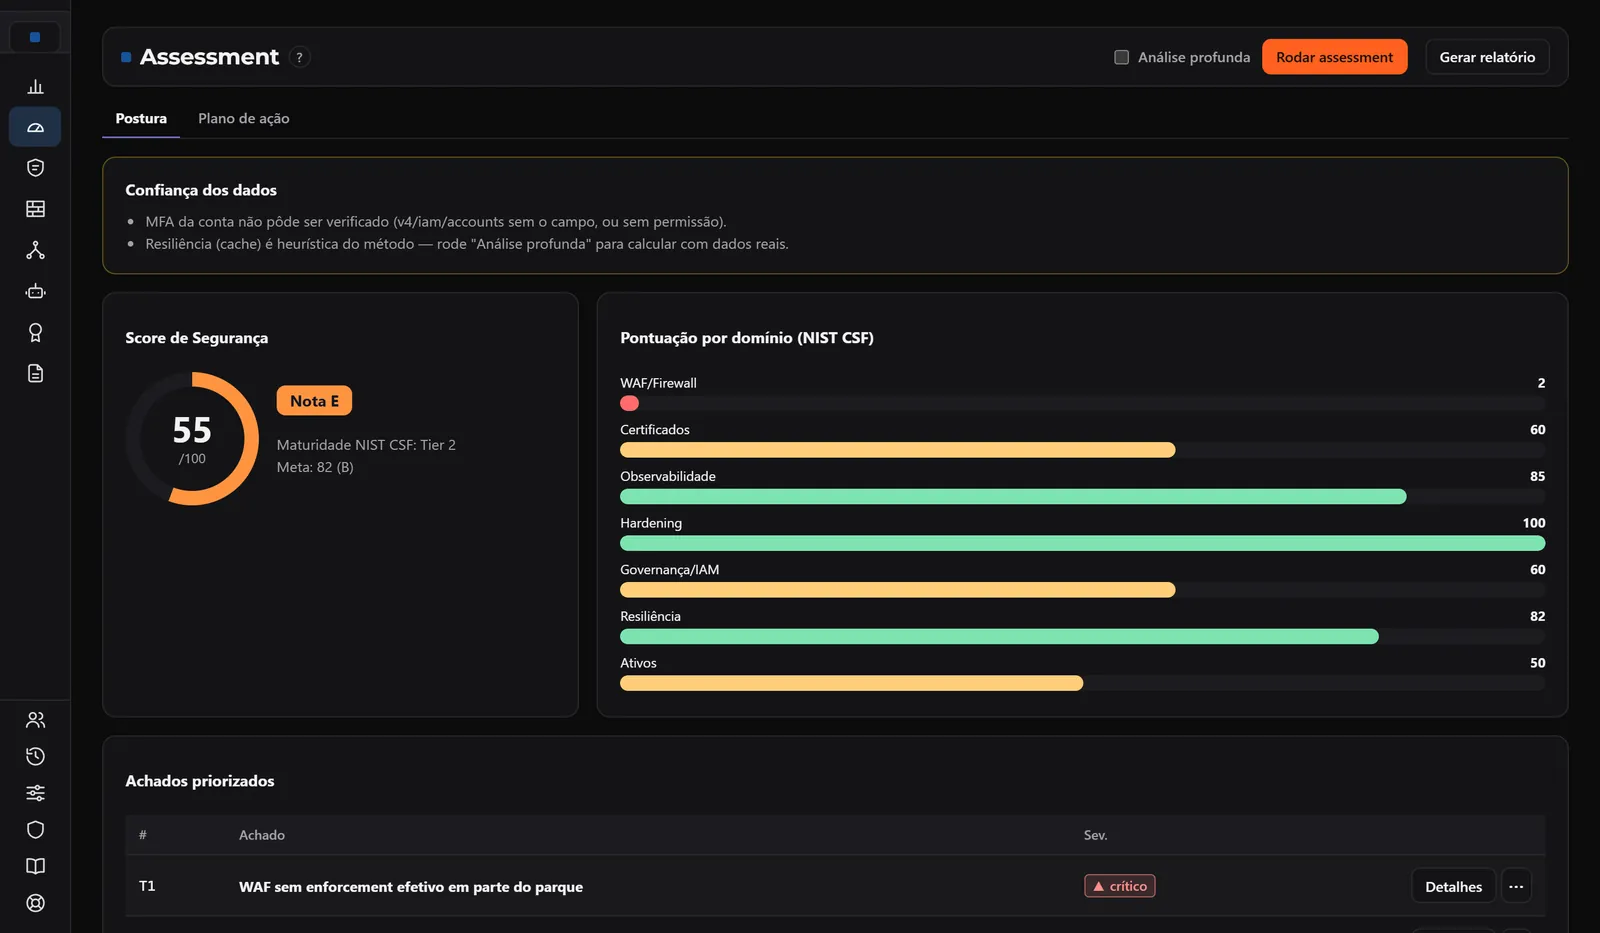
Insights reassesses the posture of every active connection every 6 hours, without anyone asking, and alerts you when something critical shows up. Each round, the 0 to 100 score is compared with the previous one: A from 90, B from 80, C from 70, D from 60, E from 50 and F below that.
- Reads the configuration, changes nothing
- Score per NIST CSF domain and maturity Tier
- Alert when a critical finding shows up
- A new round on demand, whenever you want
Compare your posture with NIST, CIS, OWASP and MITRE
Every finding is tied to the references your auditor uses: MITRE ATT&CK, OWASP Top 10, OWASP API Security Top 10, NIST CSF and CIS Controls v8, with the name and impact of each code. The Posture by framework widget groups open findings by NIST, MITRE ATT&CK or CIS category, with the previous week alongside.
- Five frameworks on every finding
- Posture by framework, week over week
- In the technical report, your configuration against good-practice targets
- Your score against your score from the previous run

Posture by framework, week over week
Take the benchmark to your dashboard: the Posture by framework widget shows open findings by NIST, MITRE ATT&CK or CIS category, with the previous week alongside, and the radar shows the OWASP API Top 10 on the same dashboard.

What to fix first
Each finding says what it is, why it matters, the evidence and what to do. Together, they become a plan by priority: urgent, important, worth fixing and quick fixes you can do right there. The history shows what was already applied, with the previous state kept.
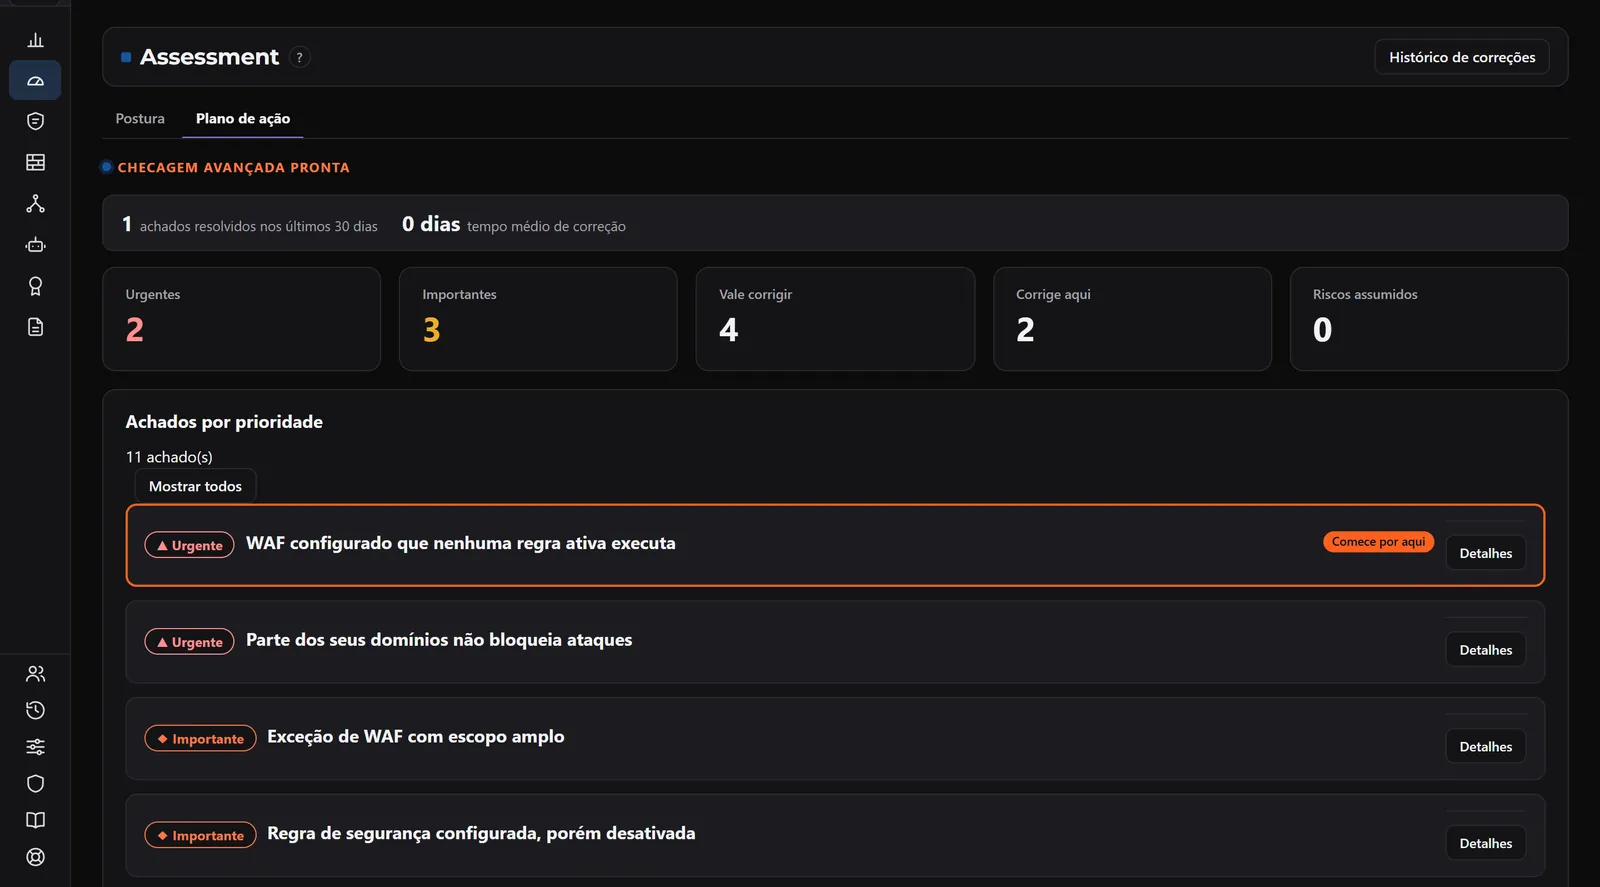
From score to decision
Accepted risk with a deadline
Accepting a risk requires a reason, an owner and a deadline of 30, 60, 90 or 180 days. A critical finding accepts 30 at most. When it expires, it goes back to open.
Active WAF test
With your authorization, harmless attack techniques hit up to 5 domains, and the result shows what the WAF blocked and what got through.
PDF report
The report comes as a PDF for leadership, with supporting evidence for CMN Resolution 4,893, BCB Resolution 85 and FAPI 2.0.
Suggested rules
To move the WAF to blocking, the assessment suggests the rules. A person on your team applies them.
Compare the rounds
The change since the previous assessment shows new and resolved findings. The methodology is versioned.
Score on the dashboard
The posture score and its progress go into the Dashboards as widgets.
What you need to use it
- Posture & Benchmark is part of WAF Manager.
- A registered connection to the provider. The assessment only reads the configuration.
- Accepting, renewing and reactivating a risk depends on your role.
Risk Scenario in Brazil
in Brazil in 2026, up 3.5% from the previous year. Visibility and fast response reduce the impact before the incident spreads.
started with a supply chain compromise, tied with phishing as the most common entry point. Knowing which third-party APIs and integrations are exposed is the first step to reducing this risk.
Know your edge's posture
See the 0 to 100 score, the score by NIST CSF domain and your account's prioritized findings.
In the conversation, you present your scenario and see the Posture & Benchmark report for it.
Talk to a specialist →