Insights Forensic Analysis
Investigate by IP, range, endpoint, host, network, country or WAF rule, with a timeline, preserved cases and SHA-256 export.
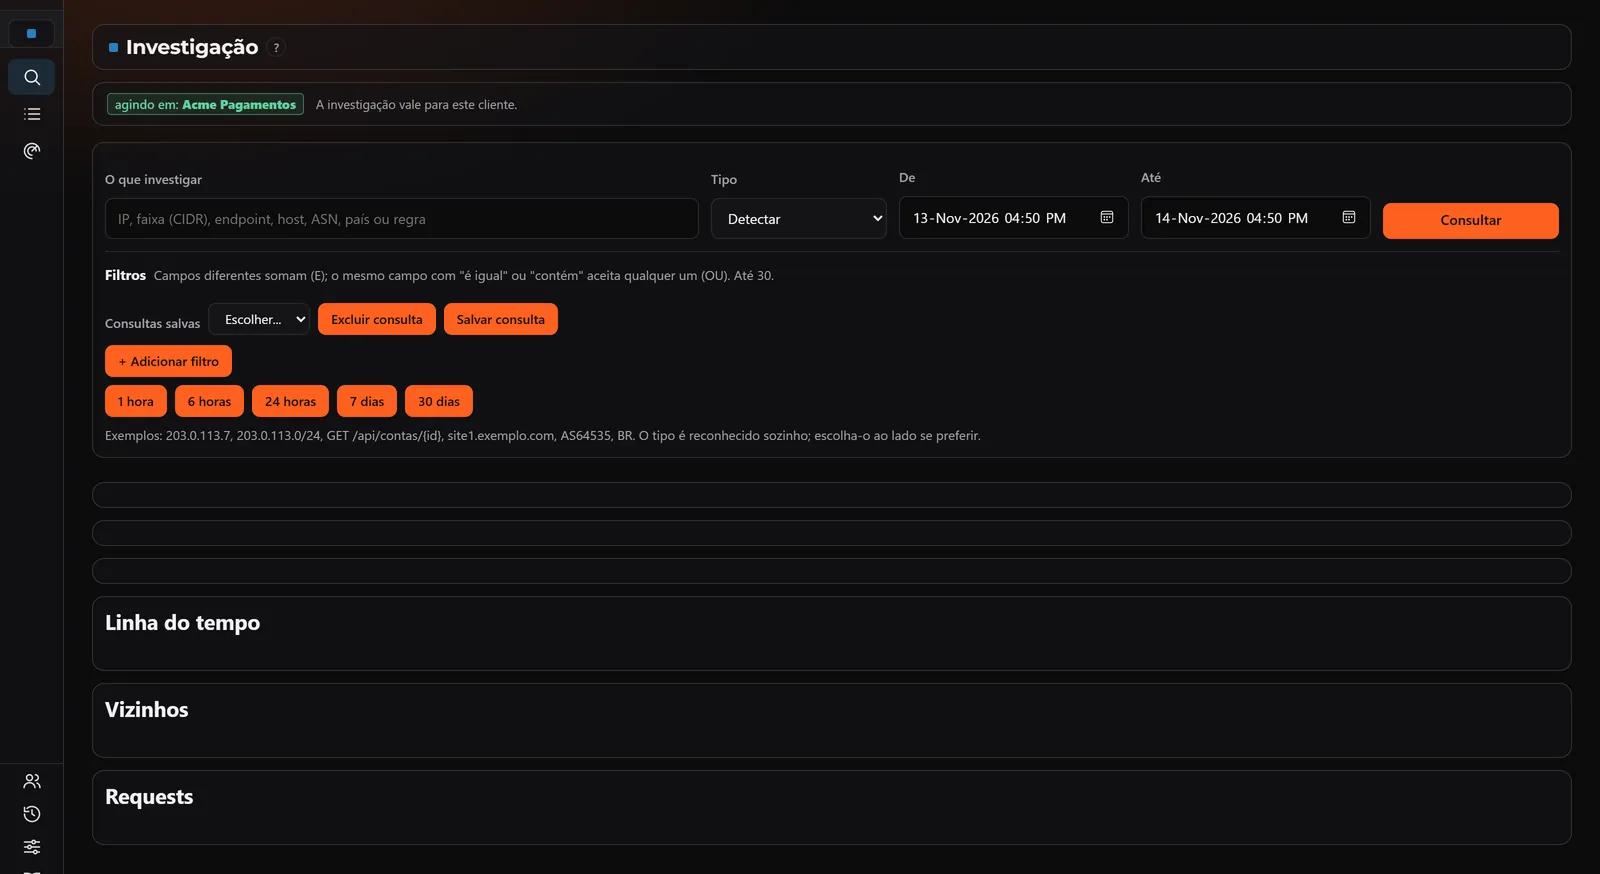
Pick the target and the period
Type an IP, a range, an endpoint, a host, a network, a country or a WAF rule, and the type is recognized on its own. Combine filters, save the query and see the target timeline, neighbors and requests.
- Ready windows from 1 hour to 30 days, or the period you choose
- Up to 30 filters per query
- Saved queries to repeat the investigation
From alert to evidence
One path, from the first signal to the file that goes to audit.
-
1
SEC HUNTER
Open in Forensics
In Hunting, one click takes the investigation with its filters and window.
-
2
INVESTIGATION
Target and period
IP, range (CIDR), endpoint, host, network (ASN), country or WAF rule, up to 90 days.
-
3
TIMELINE
What the attacker did
Session by session, in order, with the account changes made in the same period.
-
4
CASE
Evidence preserved
The investigation becomes a case, with the evidence kept and its SHA-256 fingerprint.
-
5
EXPORT
Ready for audit
PDF, XLSX, CSV, JSON, ZIP or STIX, with the reason and the chain of custody.
From target to case, with evidence
Investigations you repeat
Save the query with its filters and entity, without the dates, and run it again whenever you need. Long queries run in the background, and the result is ready when you come back.
- Up to 30 saved queries per person
- The same query, entity and period reopens the case that already exists
Cases that hold up to audit
The evidence is kept while the case is open, and for 180 days after it closes. Closing, reopening and discarding evidence are all logged, and discarding is irreversible by design.
Who uses Forensics
Incident response
Rebuild what happened, from the first access to the last, without building a query from scratch.
Evidence with custody
Hand over the case with hash, reason and a record of who exported it.
Chain of custody
Every file leaves with SHA-256 and a record of who generated it, when and why.
Export with chain of custody
Six formats
PDF, XLSX, CSV, JSON, ZIP and STIX, for the report, the spreadsheet and your intelligence tool.
Who exported and why
Every export asks for the reason and logs the user, the format, the hash, the size and the time.
Ready-made indicators
STIX carries the case's IPs and networks as indicators, ready to import into the tool you use.
Access by role
View, manage and export are separate permissions.
Fingerprint
Every exported file and every preserved case has a SHA-256 hash.
From Hunting to Forensics
The Open in Forensics button takes the investigation with its filters and window.
What you need to use it
- Forensic Analysis license, sold separately.
- Insights log storage enabled: Forensics reads the stored events, within the retention you set.
Risk Scenario in Brazil
in Brazil in 2026, up 3.5% from the previous year. Visibility and fast response reduce the impact before the incident spreads.
started with a supply chain compromise, tied with phishing as the most common entry point. Knowing which third-party APIs and integrations are exposed is the first step to reducing this risk.
Take the incident to audit with exportable evidence
For those who take the incident to audit, legal or the board: exportable case evidence.
In the conversation, you present your use case and see how Insights Forensic Analysis fits it.
Talk to a specialist →