Insights API Security
Know which APIs your company exposes. Insights builds the inventory from the actual traffic of your edge and gateways, documents each API and flags the risk with the request that proves it.
A live inventory of your APIs
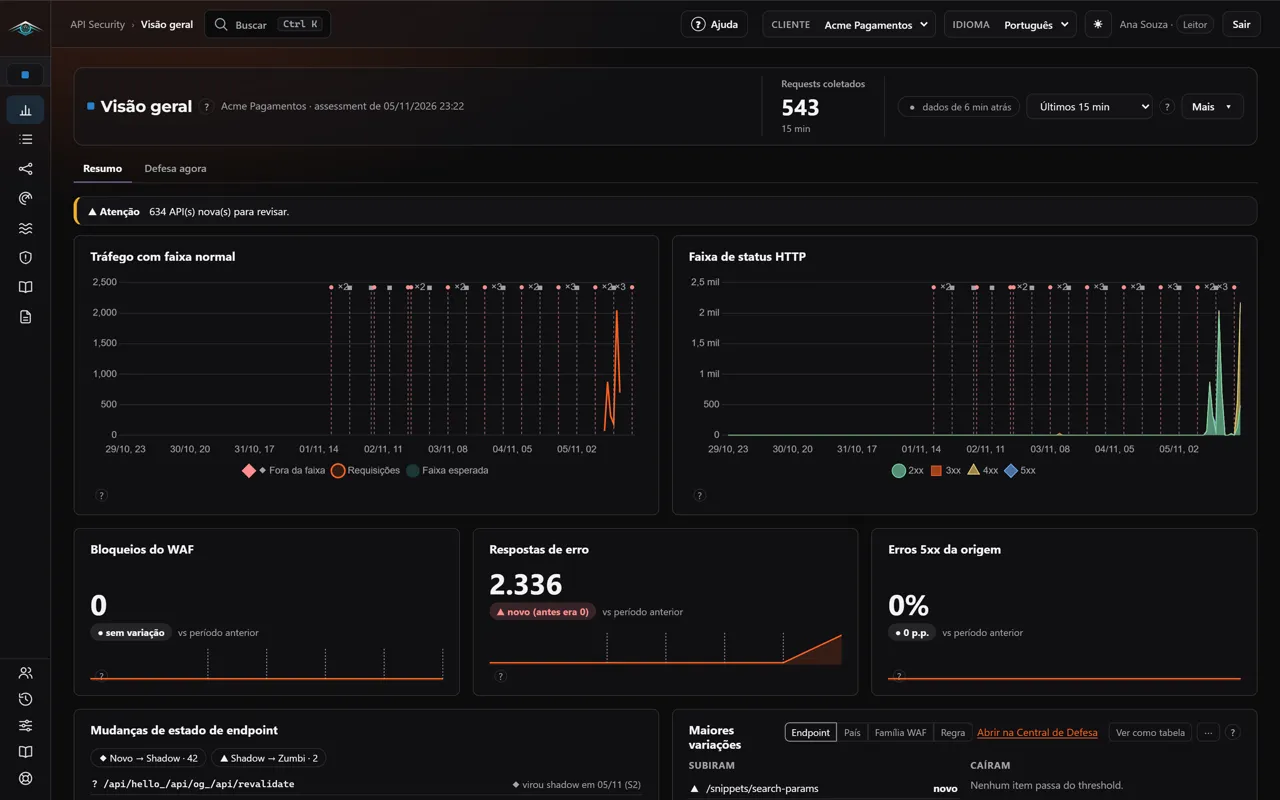
LibertySec connects Insights to your edge, your WAF and the API gateways you already use, and the inventory is built from traffic. Each endpoint is classified as legitimate, shadow (outside the spec or never reviewed) or zombie (marked as retired and still receiving calls), with the reason written out.
- Classification against the spec, endpoint by endpoint
- Shadow and zombie, with the reason for each
- An inventory that follows the traffic
From discovery to fix
The path of every call
From consumer to origin, through the edge, the WAF and the gateway, with consumers by country and by network in 24-hour or 7-day windows and a detail panel on each node.
Documentation built from traffic
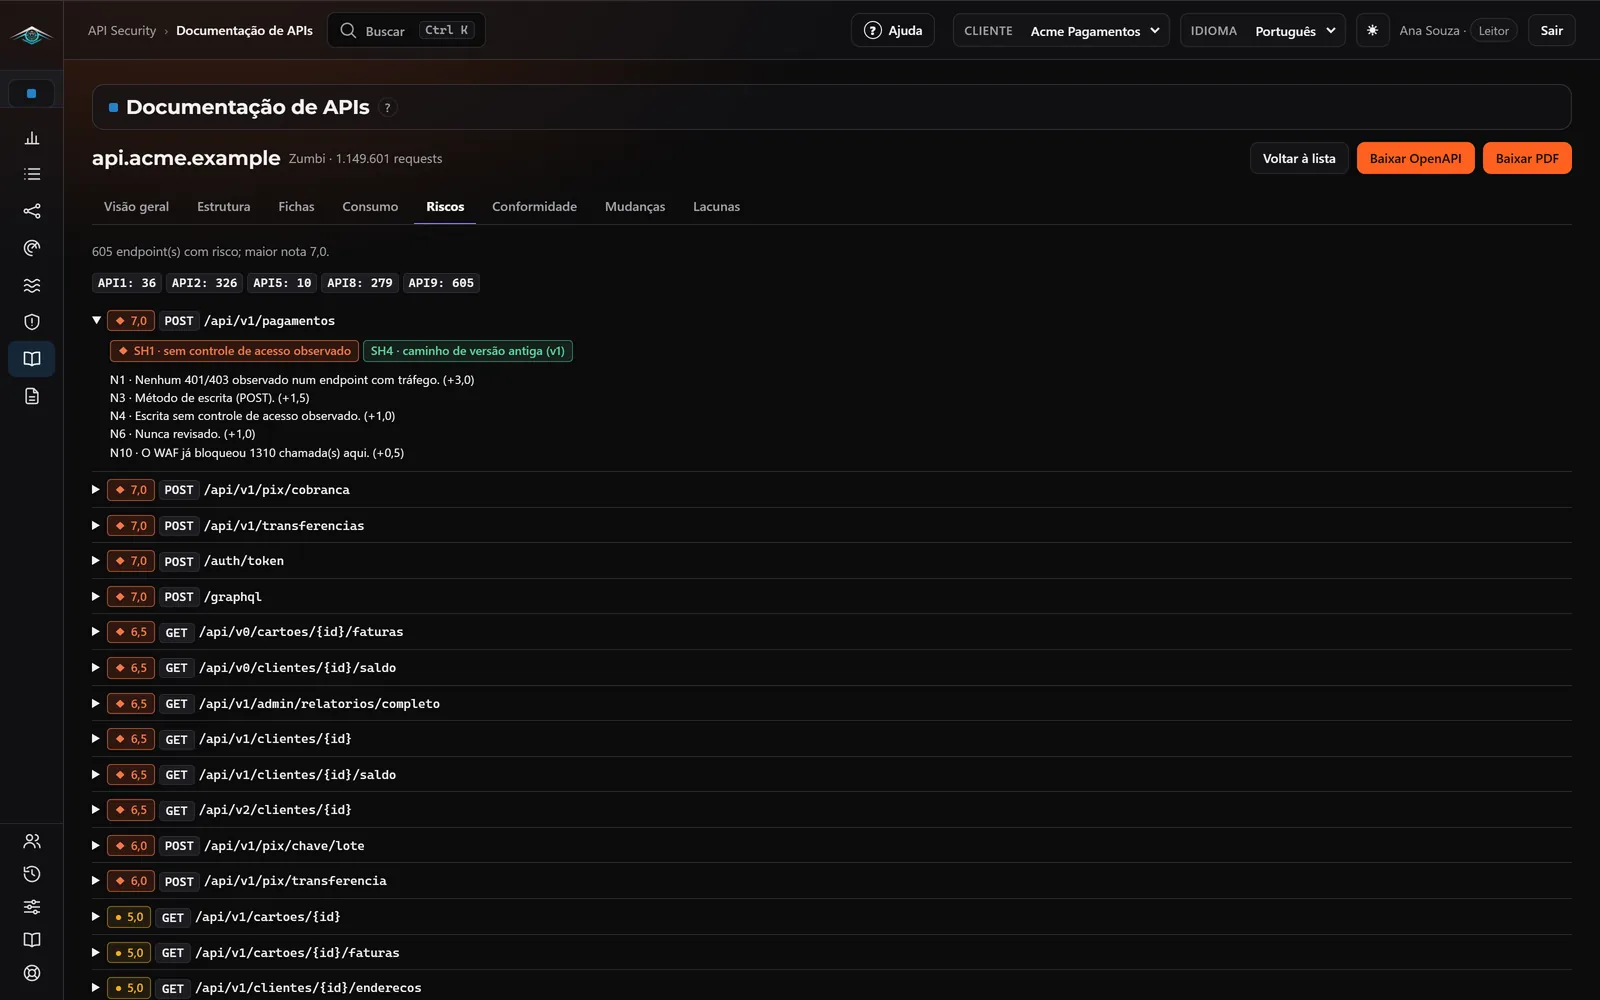
Each API gets its own documentation in 8 tabs: Overview, Structure, Sheets, Consumption, Risks, Compliance, Changes and Gaps. OpenAPI to download, an API PDF and what changed since the last version.
15 ready-made detection templates
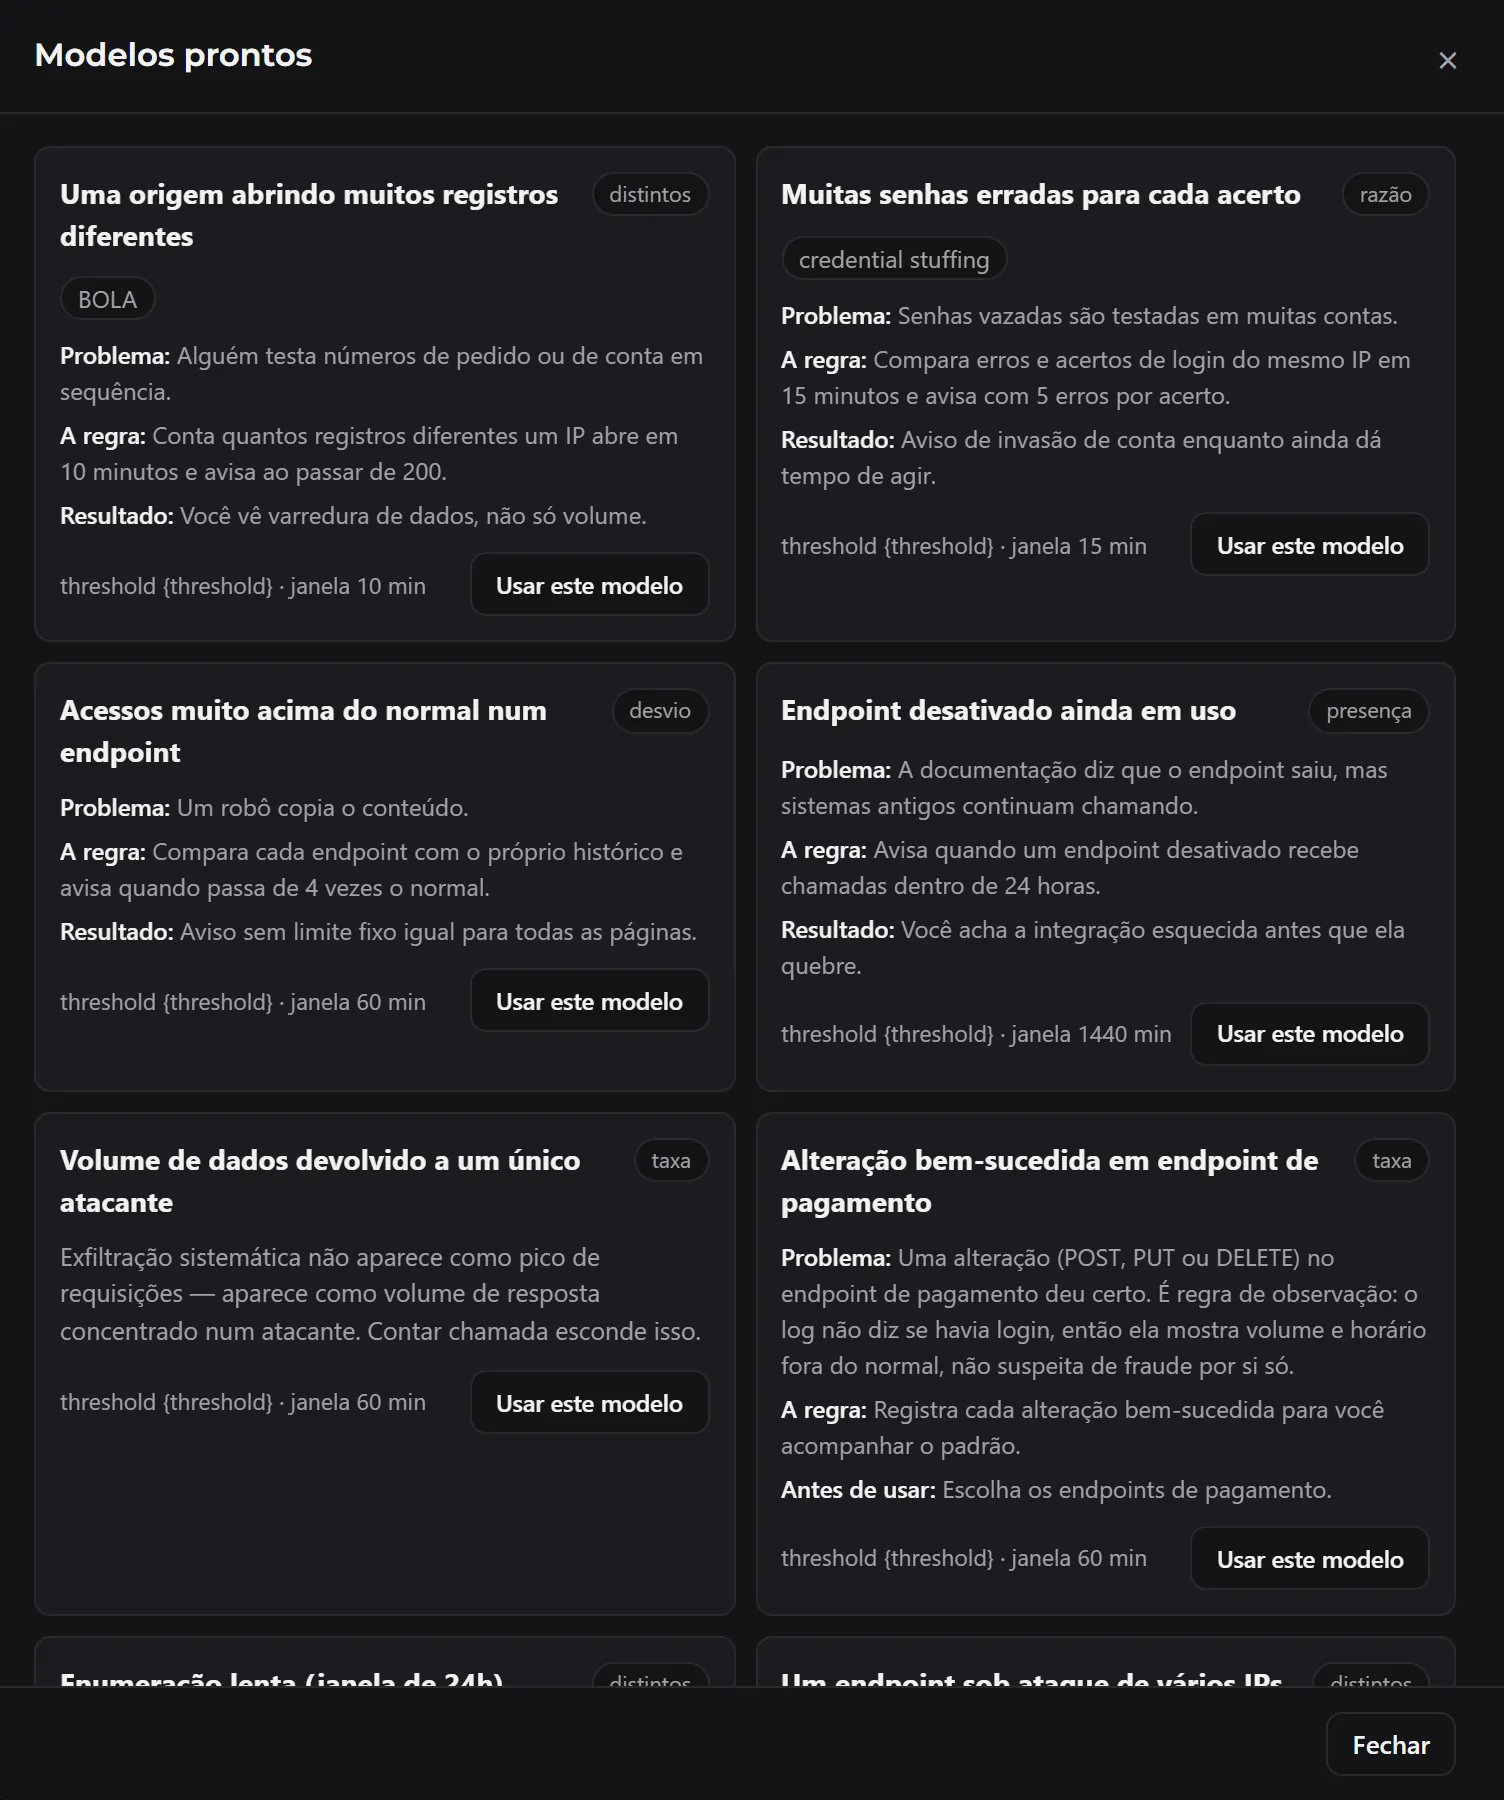
Route scanning, many wrong passwords for each hit, slow enumeration, data volume returned to a single attacker, a retired endpoint still in use and access to many objects per consumer (BOLA). Each template explains the problem, the rule and the result, and starts off.
See your APIs
A LibertySec specialist connects your edge and shows the inventory with your traffic.
Each endpoint with its own normal
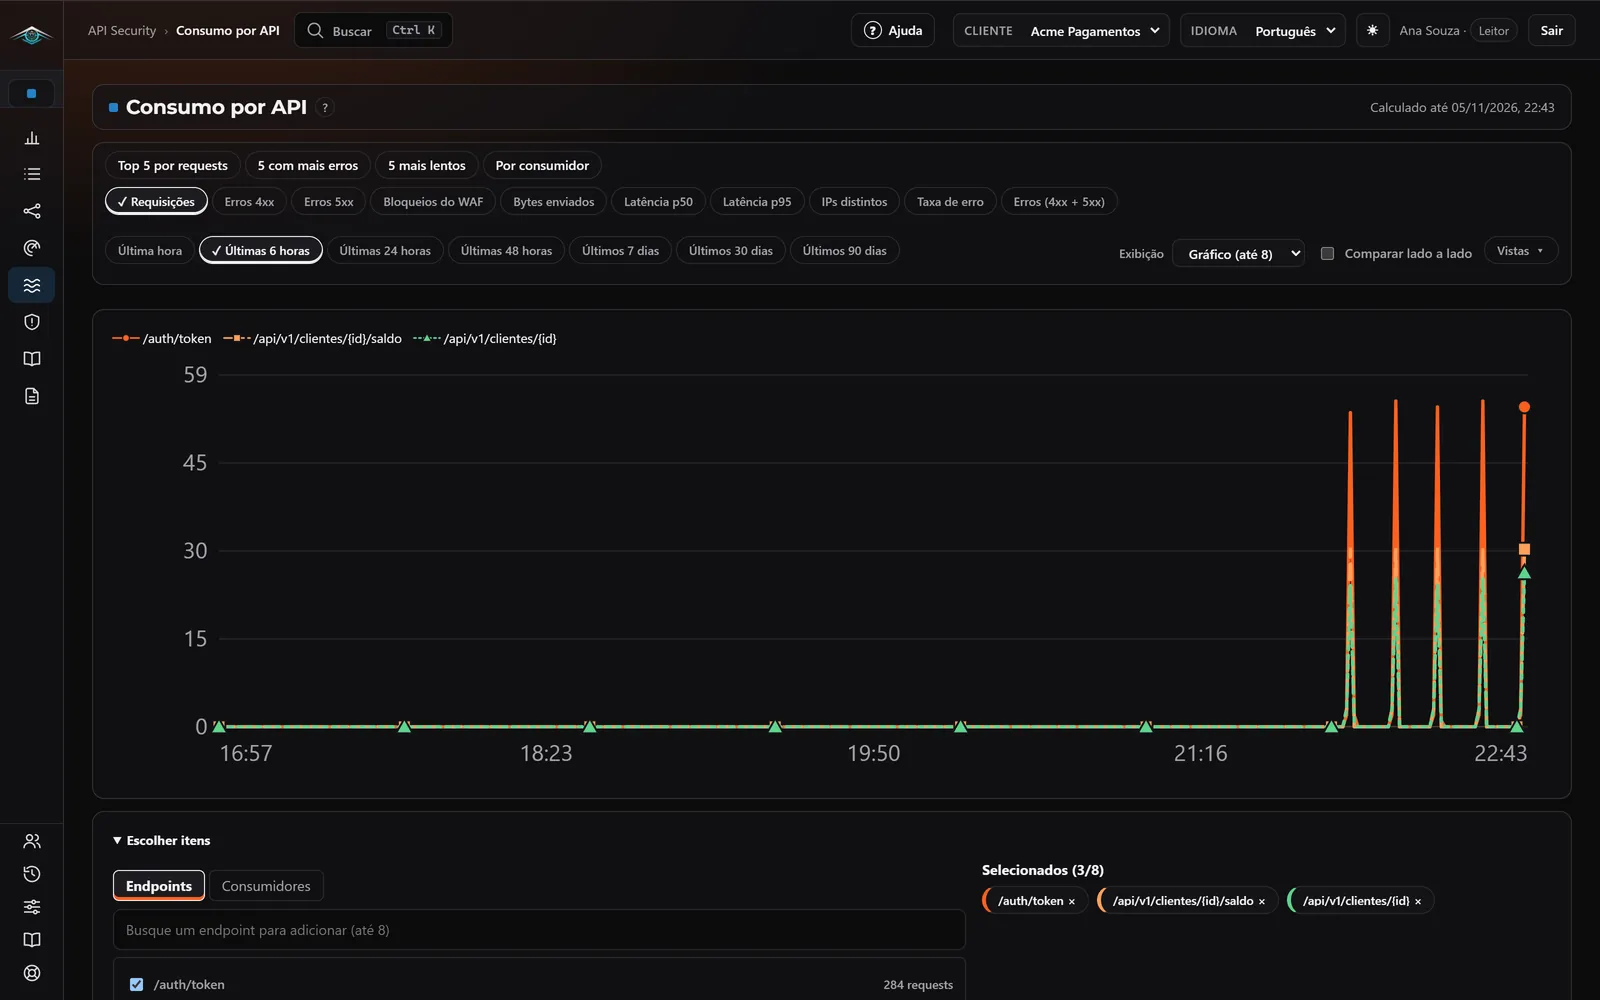
Each endpoint's normal is calculated by hour of the week, over 28 days, for requests, 4xx and 5xx errors, data volume and p95 latency. A deviation opens when the value leaves the range and closes on its own when it returns.
All 10 categories, with evidence
Covers all 10 categories of the OWASP API Security Top 10: 8 with automatic detection, each finding with the request that backs it, and 2 with guided verification.
The fix is ready, a person confirms
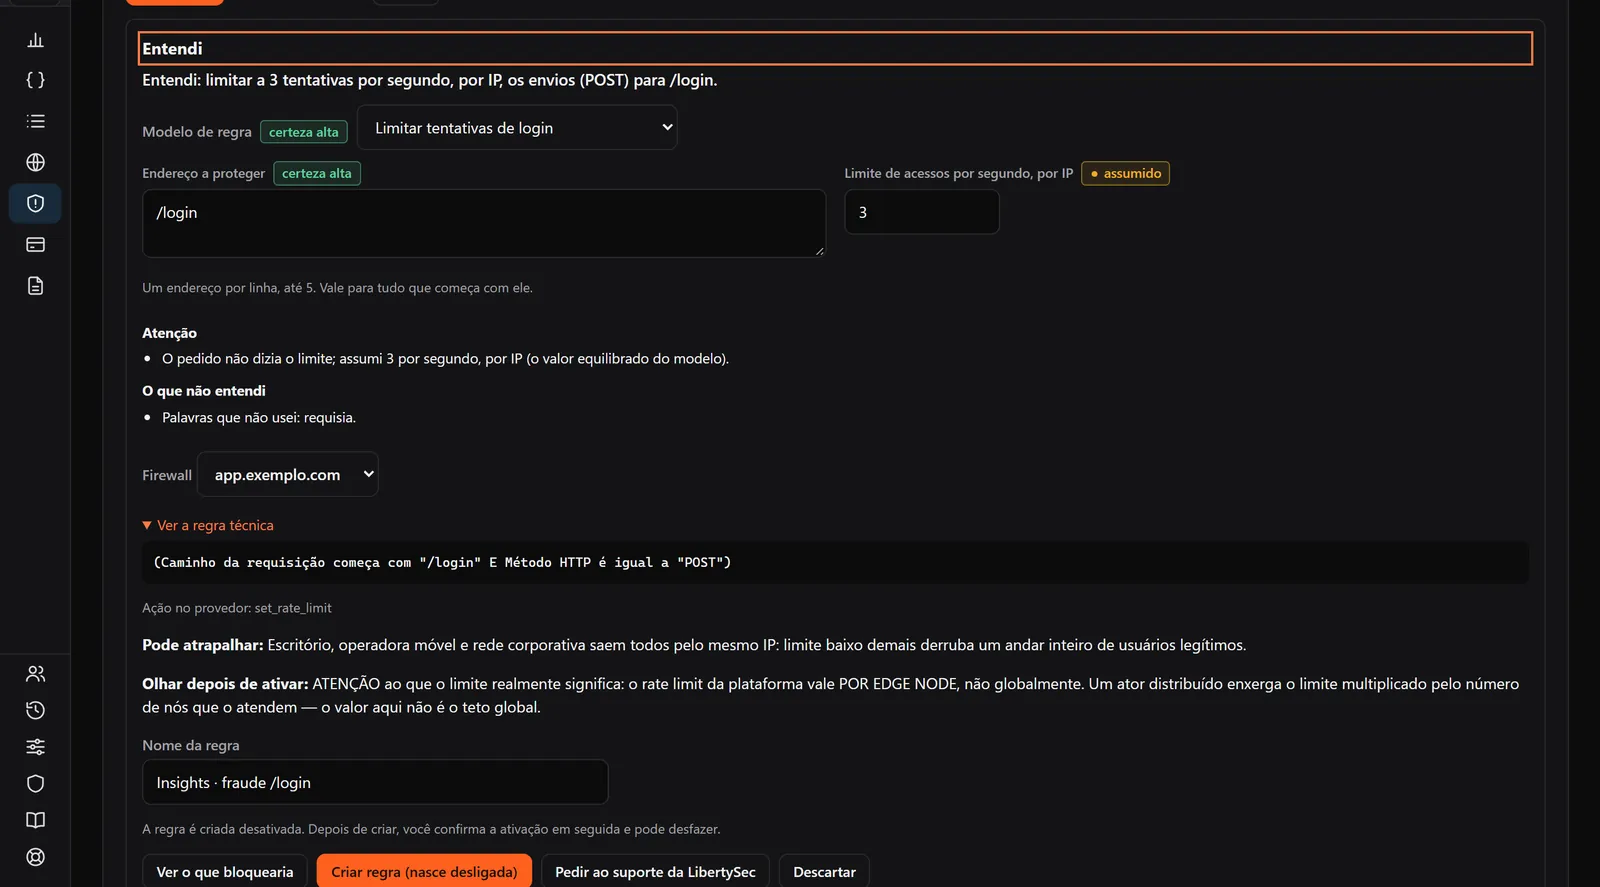
With the edge connected with management, the finding comes with the fix ready for a person on your team to confirm, and the action is logged with an audit trail. Ask for the rule in your own words: Insights shows what it understood, and the rule starts off.
Tests, deadlines and evidence
Assisted BOLA test
With two test credentials, Insights checks whether one identity can access the other's objects. GET only, up to 10 endpoints and 150 requests per run, and the response body is never stored.
Active test of WAF protection
With the edge connected with management, harmless attack techniques show what the WAF blocks and what it lets through.
Accepted risk with an owner and a deadline
Reason, owner and a deadline of 30, 60, 90 or 180 days. When it expires, the risk reopens on its own.
Spec versus production
The declared OpenAPI, including the one from your CI/CD pipeline, compared with what the edge sees.
Usage per API
Requests, errors and latency per endpoint, with the consumer's identity when a gateway is connected.
Reports
Executive report, API PDF and supporting evidence for banking regulation.
Insights in 3 minutes
 Narrated in Portuguese · 3 min
What you need to use it
- API Security license.
- Edge, WAF or API gateway connected. LibertySec makes the connection, and a specialist confirms with you how it fits your environment.
- The ready-made fix and the active test of WAF protection require the edge connected with management.
Risk Scenario in Brazil
in Brazil in 2026, up 3.5% from the previous year. Visibility and fast response reduce the impact before the incident spreads.
started with a supply chain compromise, tied with phishing as the most common entry point. Knowing which third-party APIs and integrations are exposed is the first step to reducing this risk.
Know which APIs your company exposes
Tell us about your environment: edge, WAF and gateways. A specialist explains what Insights shows in it and how the connection is made.