Insights Bot Defense
Ready-made detectors and templates to tell automation from people, counting by source and window, with the proposed rule for a person to confirm.
Automation recognized by behavior
Detectors count events by source in a window and compare against a threshold: route scanning, fast crawling, fake crawler and the sequence of login followed by a sensitive action. They alert or propose, and the rule only takes effect after a person turns it on.
- Automation User-Agent: 20 in 10 minutes
- Fast crawling per IP: 300 in 5 minutes
- Route scanning per IP: 50 in 10 minutes
- Login followed by a sensitive action: 3 in 15 minutes
- Thresholds are a starting point, tuned to your traffic

Ready-made rule templates
Four templates to start: send a sensitive address to the provider's Bot Manager challenge, slow down automation tools, block networks already flagged and limit a source's requests. Each one opens in the builder already filled in.
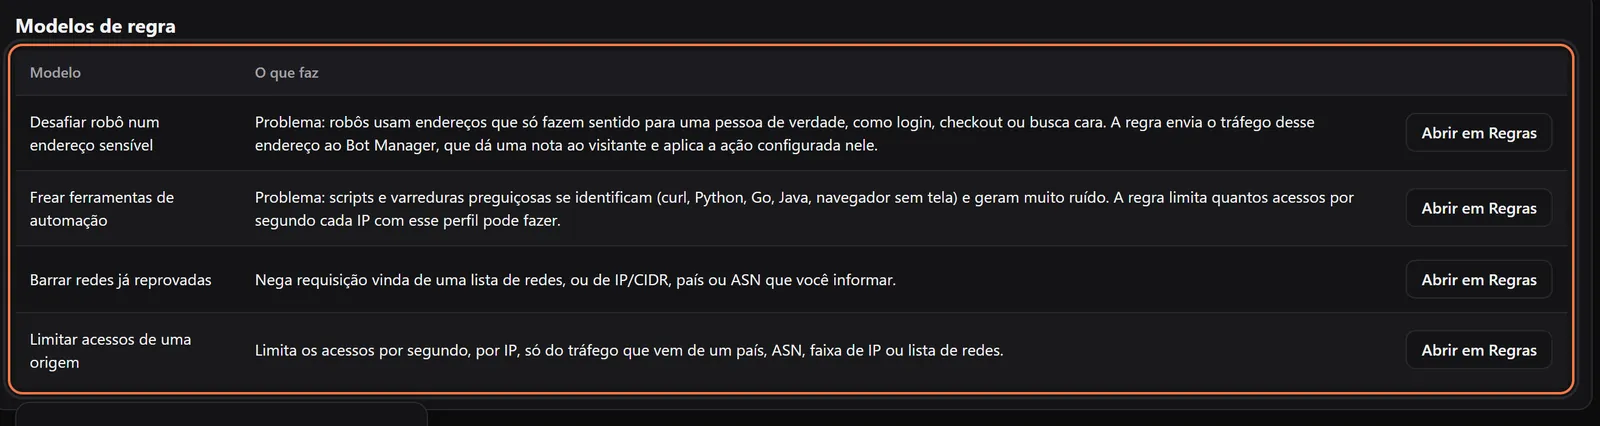
From count to rule
Build your rule
Choose the source (IP, network or User-Agent), the window from 1 to 1440 minutes and the threshold.
Bot items
The most active IPs, networks and User-Agents in the last 1, 6 or 24 hours, with the network type, such as hosting and cloud. Each one becomes a rule in one click.
Adopt and tune
Adopting a detector copies the rule, off, for you to tune and turn on.
A person confirms
Bot Manager configuration goes through a preview and strong confirmation, and is logged.
Bot Manager on the same panel
The provider's Bot Manager configuration, reputation and fingerprint, where it offers them.
Rules from your normal
Rules that compare against the baseline are available with at least 14 days of history.
What you need to use it
- Bot Defense license, a separate module.
- Insights log storage enabled: the detectors read the collected events.
- The provider's templates and the Bot Manager configuration require the edge connected with management.
Risk Scenario in Brazil
in Brazil in 2026, up 3.5% from the previous year. Visibility and fast response reduce the impact before the incident spreads.
started with a supply chain compromise, tied with phishing as the most common entry point. Knowing which third-party APIs and integrations are exposed is the first step to reducing this risk.
See the abuse on your critical routes
Bring your login and payment routes to our team and see which rules make sense for them.
In the conversation, we look at your critical routes and the rules Bot Defense proposes for them.
Talk to a specialist →